FDA’s Postmarket Cybersecurity Guidance Is Due for an Update.
What Changes When Your Devices Are Already in the Field By Ken Zalevsky, VP and GM, C2A Security A revision would likely do more than
" " indicates required fields

What Changes When Your Devices Are Already in the Field By Ken Zalevsky, VP and GM, C2A Security A revision would likely do more than
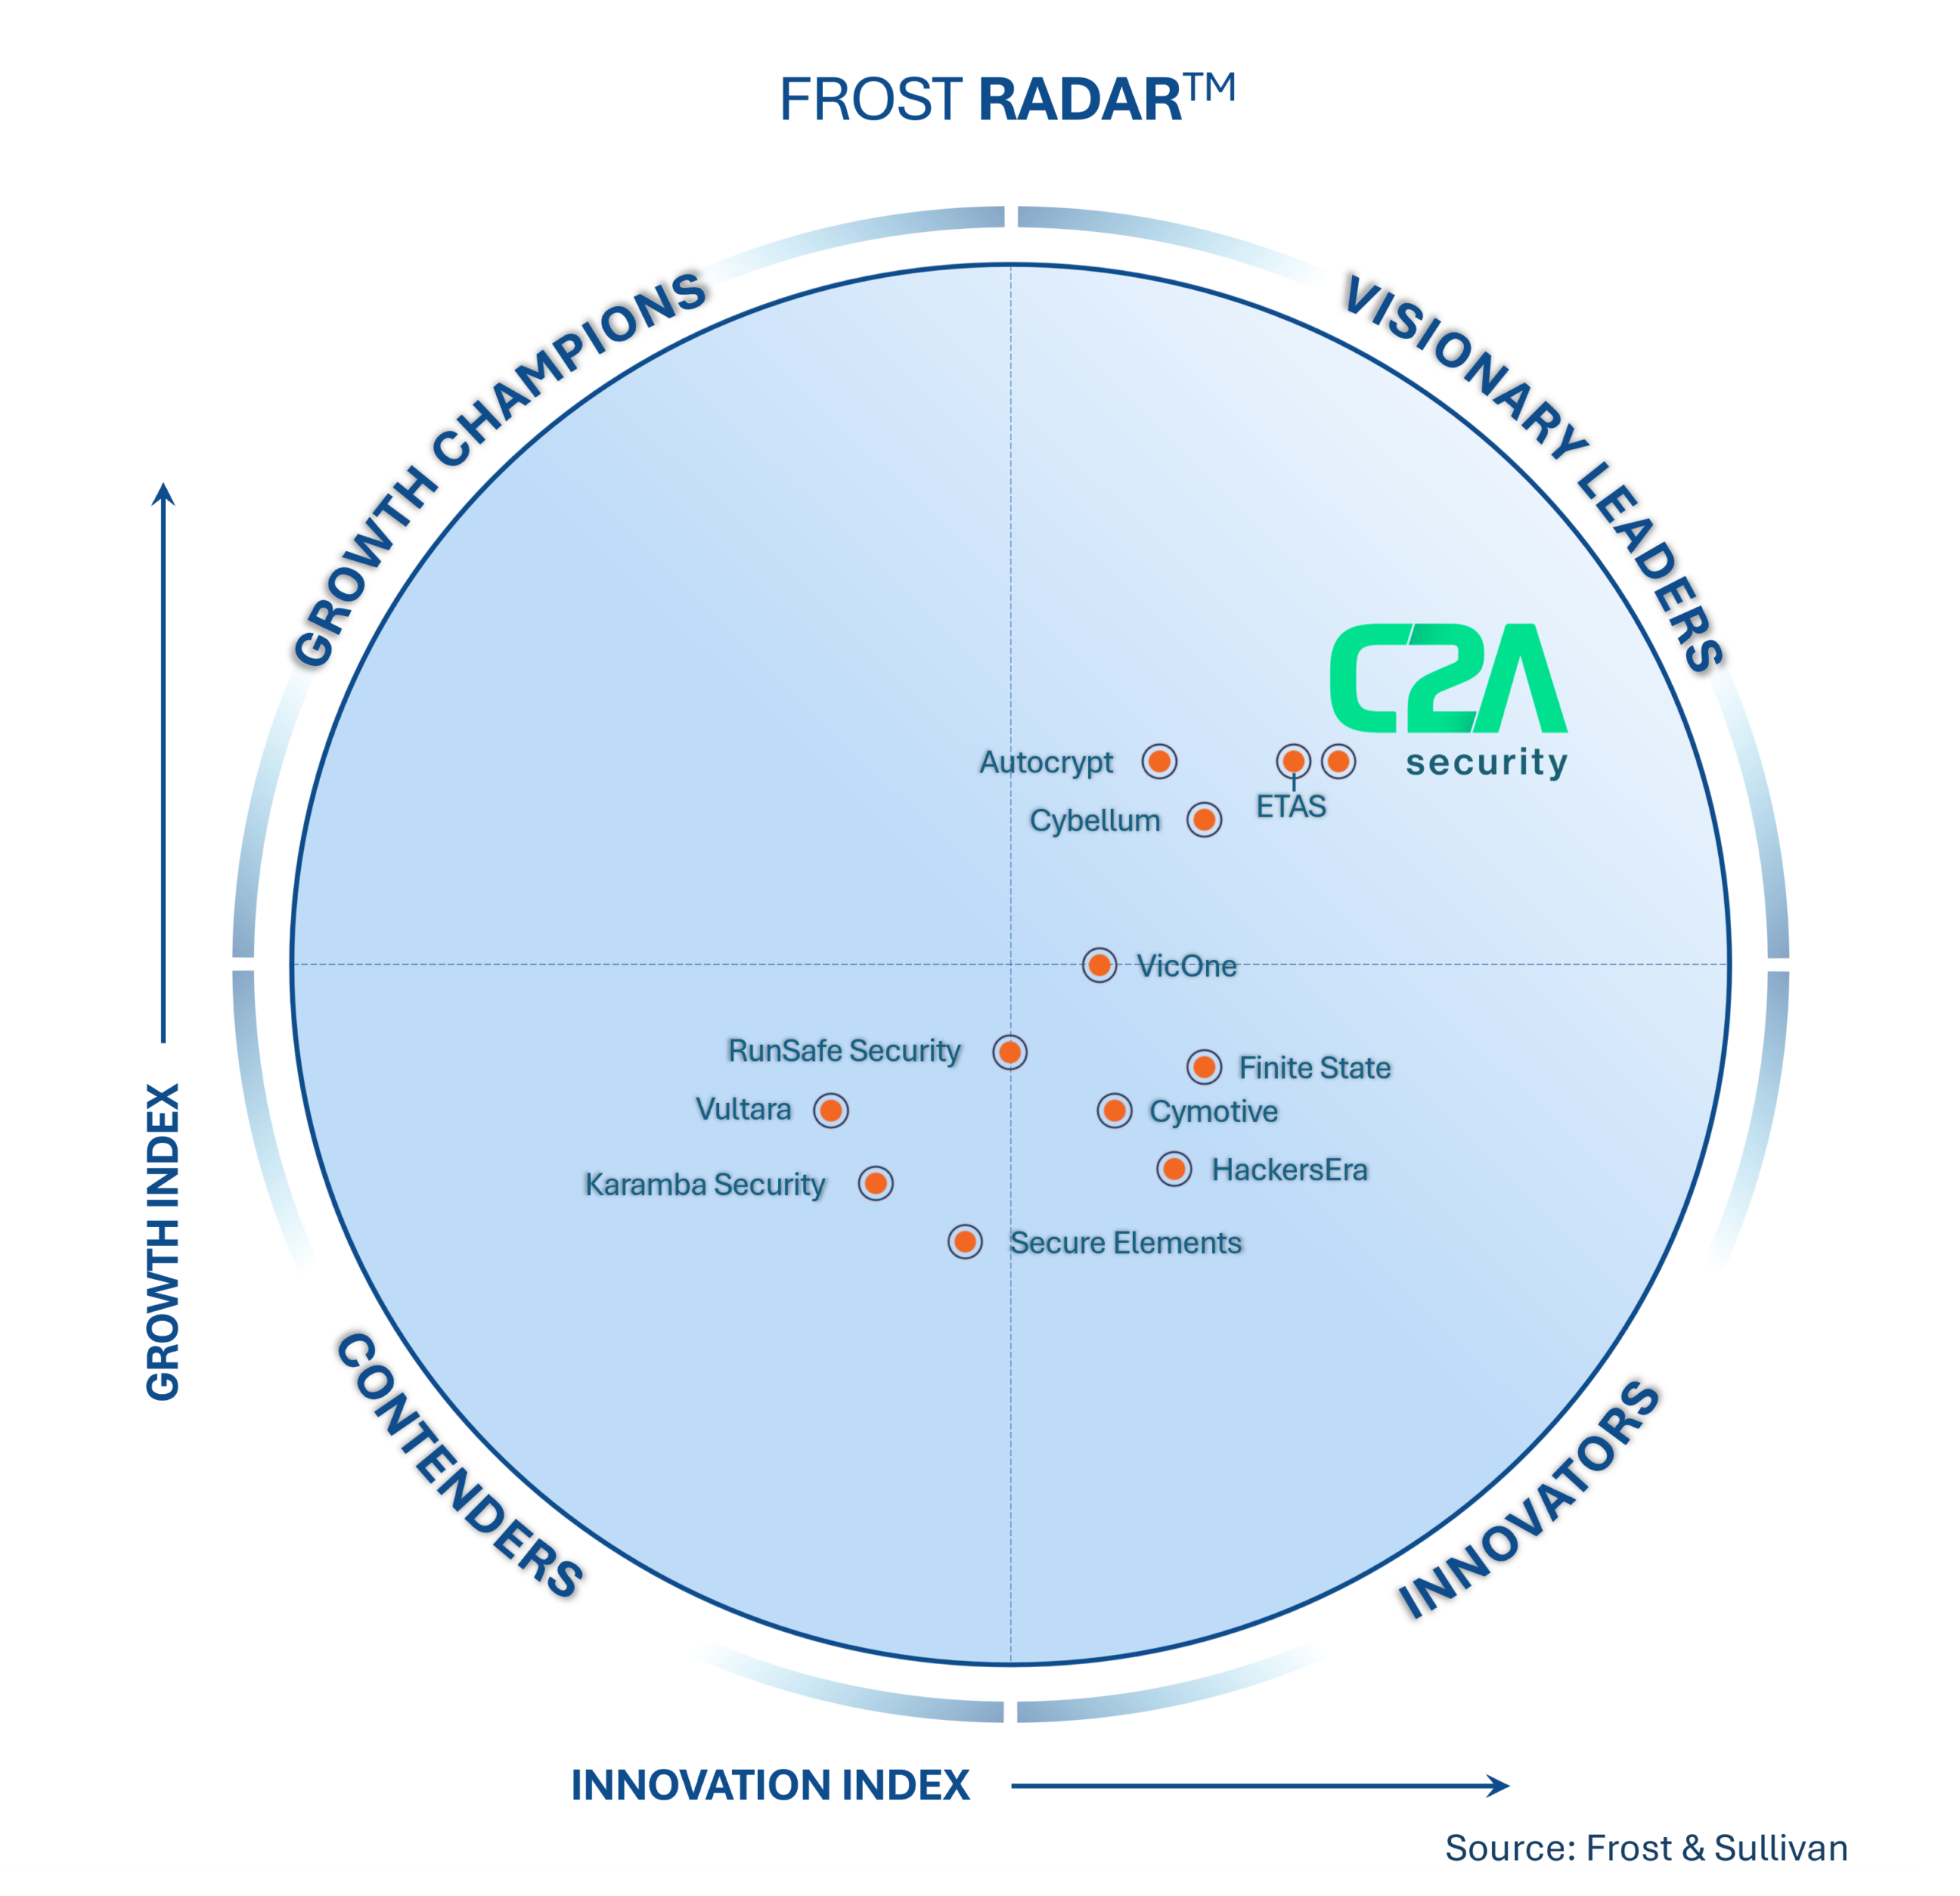
Jerusalem, Israel, August 25, 2026 — C2A Security, the only context and AI-driven product security orchestration platform addressing the needs of software-defined products and cyber-physical
Five agencies, the Siemens S7 advisory, and the product security question underneath it On August 19, 2026, five U.S. federal agencies signed the same document.
Lubadel brings more than 25 years of healthcare technology, product security and regulatory experience to support C2A Security’s strategy across medical devices and other cyber-physical
The future belongs to systems that can prove provenance, context and chain of custody. The Growing Challenge of Digital Trust Artificial intelligence is changing the
SBOM as a Global Initiative SBOMs are no longer viewed as a best practice; they are now essential for OEMs to maintain software supply chain
In July 2025, a highly prolific breach made waves in the cybersecurity world when the U.S. National Nuclear Security Administration (NNSA) confirmed that it had
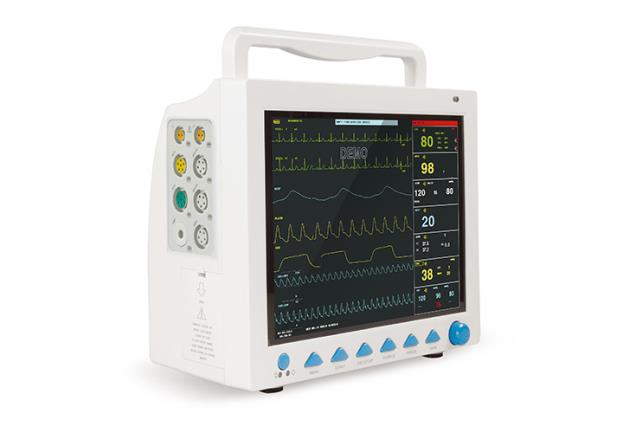
In early 2025, security researchers uncovered a critical vulnerability in the Contec CMS8000 patient monitor system – an affordable, widely deployed device in hospitals and
The interconnected healthcare sector is facing a growing threat from IoT devices. Check Point Research uncovered a 45% YoY surge in attacks on healthcare organizations