FDA’s New Medical Robotics Discussion Paper: Why Cybersecurity Must Be Evaluated End to End.
FDA’s new discussion paper on medical robotics carries one message cybersecurity teams should not miss: risk cannot be assessed one component at a time. On
" " indicates required fields

FDA’s new discussion paper on medical robotics carries one message cybersecurity teams should not miss: risk cannot be assessed one component at a time. On
What Changes When Your Devices Are Already in the Field By Ken Zalevsky, VP and GM, C2A Security A revision would likely do more than
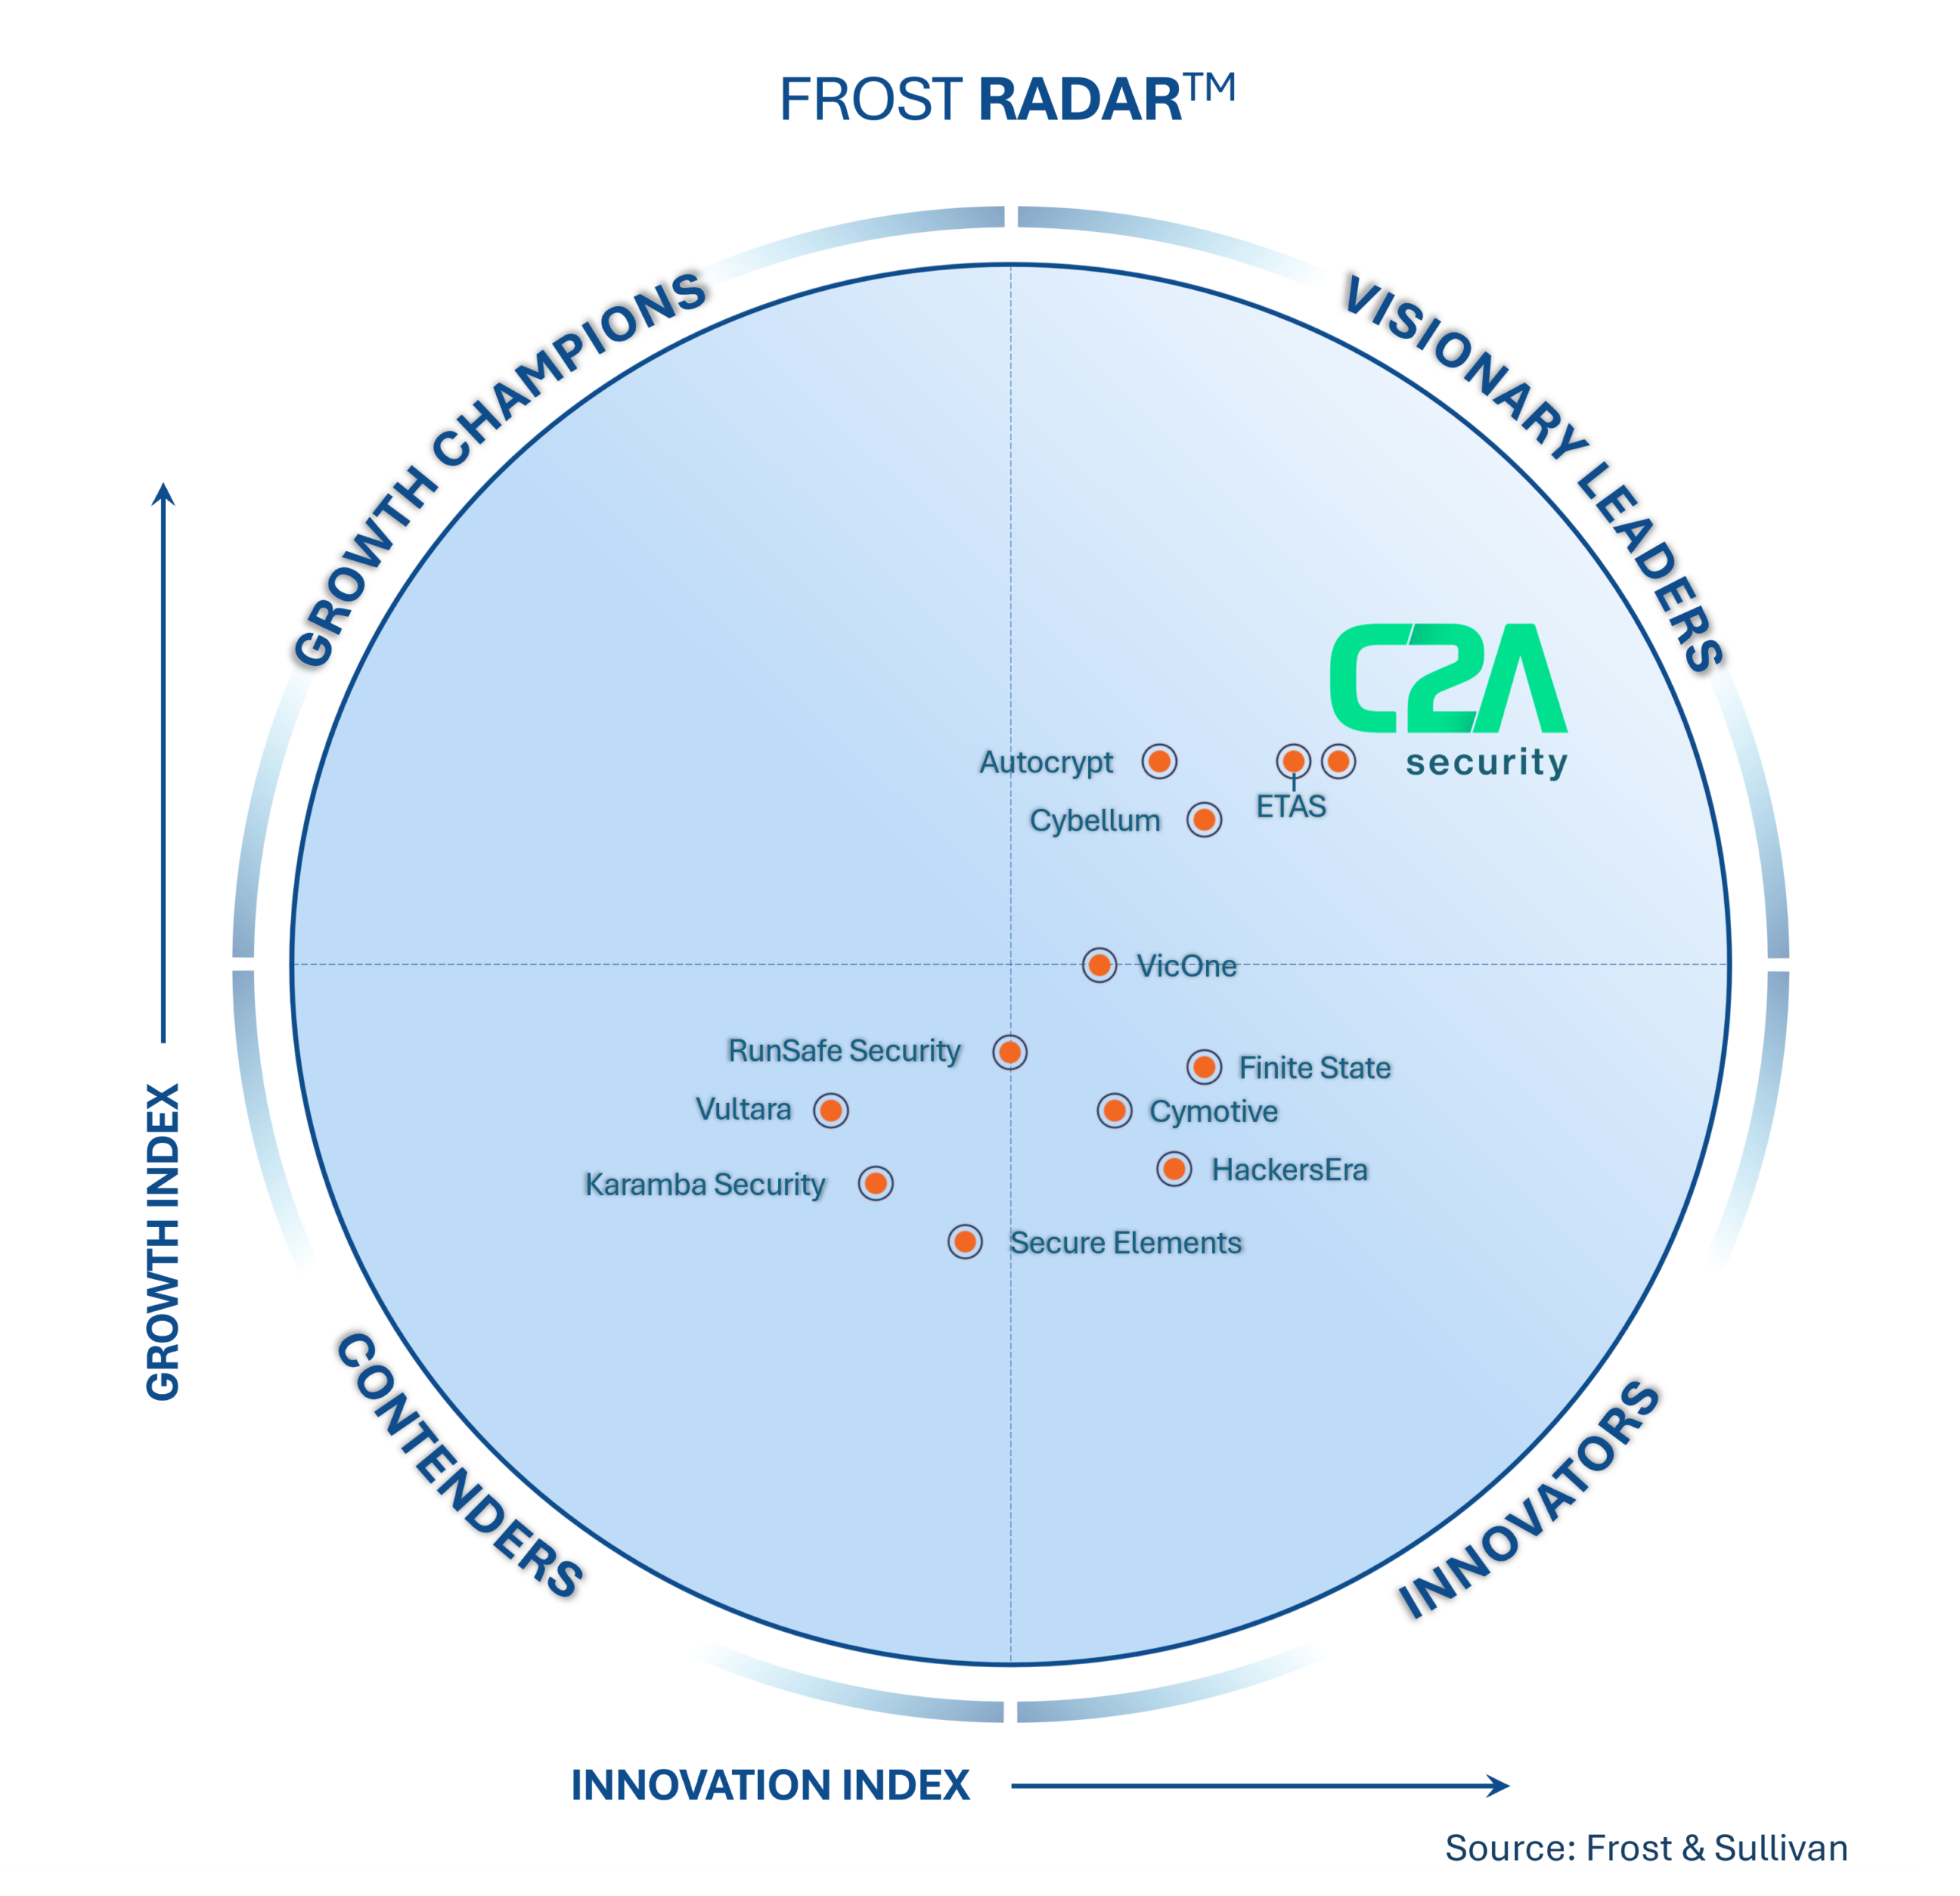
Jerusalem, Israel, August 25, 2026 — C2A Security, the only context and AI-driven product security orchestration platform addressing the needs of software-defined products and cyber-physical
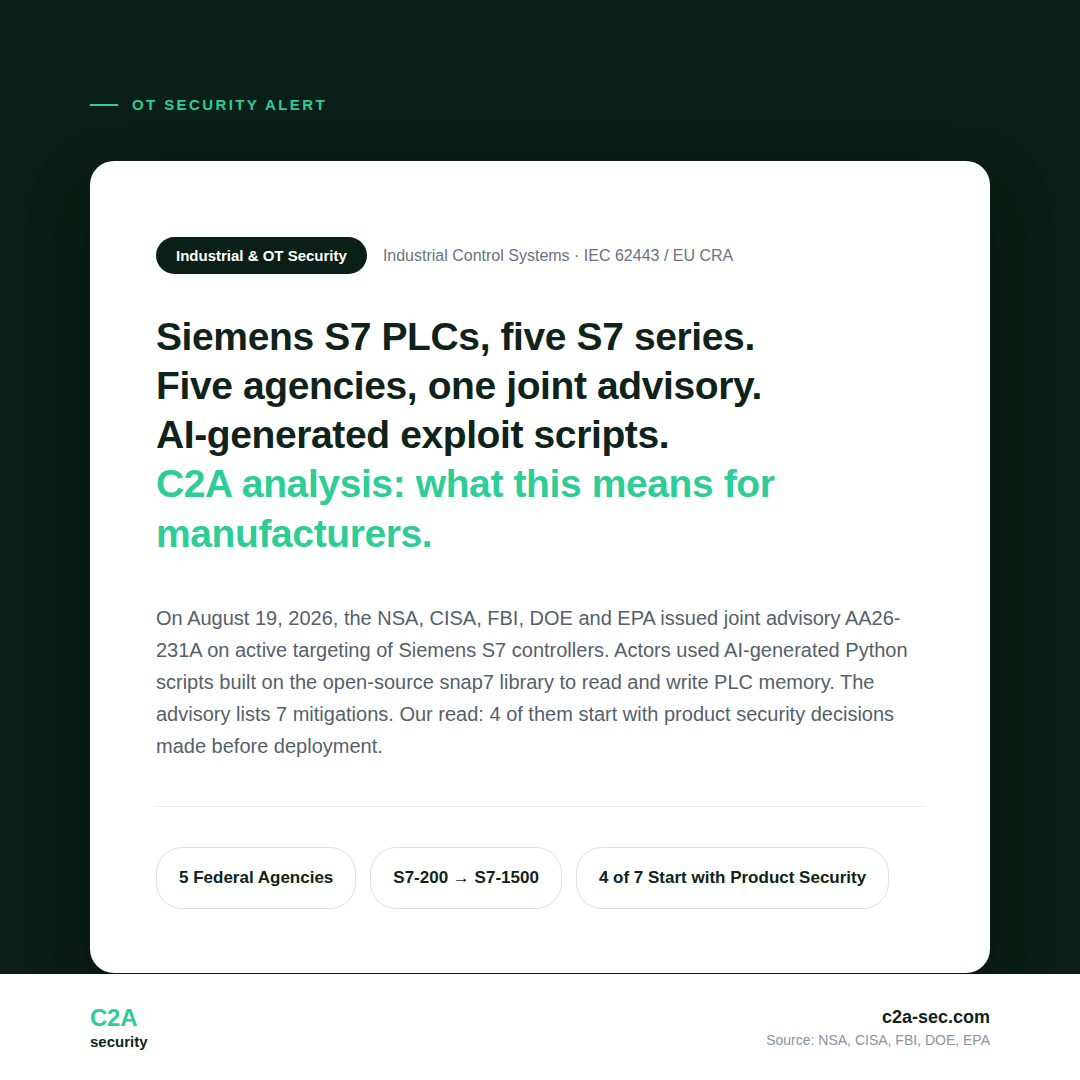
Five agencies, the Siemens S7 advisory, and the product security question underneath it On August 19, 2026, five U.S. federal agencies signed the same document.
The future belongs to systems that can prove provenance, context and chain of custody. The Growing Challenge of Digital Trust Artificial intelligence is changing the
C2A Security · July 2026 · 10 min read Executive Summary Cybersecurity is no longer measured solely by an organization’s ability to prevent vulnerabilities. Increasingly, regulators, customers, and
On this episode of Decoding Product Security series, Gilad Bandel, VP Cybersecurity, hosted Matthias Welzmiller, Unit Head, Vehicle Cybersecurity and Safety, at TRATON (MAN). Gilad
The C2A Security team compiled a list of the best medical and healthcare cyber podcasts that every medical security professional and MDM should bookmark. We’ve
The healthcare sector is facing growing risks from the interconnected Internet of Medical Things (IoMT), where vulnerabilities in a single device can expose entire networks