" " indicates required fields
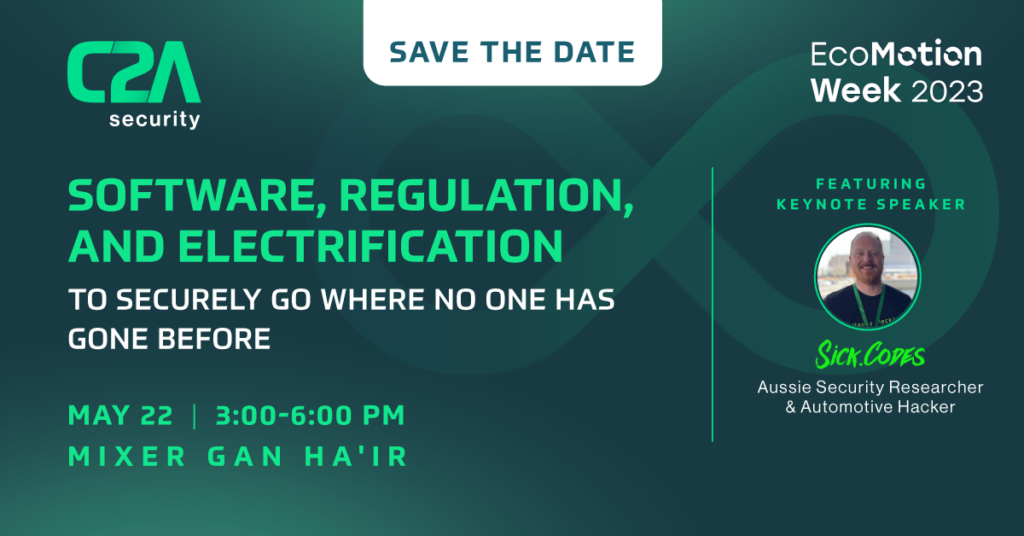
On Monday, May 22, 2023, we’ll host an exclusive side-event (bold & hyperlink to reg page) during EcoMotion Week featuring keynote talks from renowned hacker Sick Codes, Foxconn & Mobility in Harmony’s Joe Cheng and our own Roy Fridman. During the intimate afternoon event we’ll explore the convergence of software, regulation, and electrification, how security is intertwined into them. We’ll also present what are customers and partners are doing to respond to these challenges, by speeding up software release times and building trust with consumers, while adhering to regulation and staying compliant.
Register here to secure your seat at the event.
We caught up with Sick this week to get his perspectives on some of the transformational changes the automotive industry is undergoing and their impact on security.
Sick Codes will also speak during EcoMotion Main Event on Tuesday, May 23, at Expo Tel Aviv and will be available at our booth (364) throughout the day.
To hear more from Sick Codes, register to our exclusive side-event during EcoMotion Week, on Monday, May 22 in Tel Aviv click here.
Dynamic threat modeling and risk assessment aligned with global regulations
LLM-agnostic generative AI layer powering automation across every module
Aggregated threat feed contextualized against your actual products
Generate, manage, and triage all BOMs and vulnerabilities across the lifecycle
Quantitative optimization of mitigation strategy and security control allocation
Configurable dashboards and reports across every EVSec data layer
Extract software composition and risk from firmware and binaries without source code
Optimized anomaly detection for Ethernet and CAN, plus ECU runtime protection
Quantify and manage cybersecurity risk for products operating in the field
Enrich SOC events with deep product and architecture context
Context-driven test and validation with intelligent fuzzing, integrated into CI/CD
AI-powered static analysis integrated into CI/CD with reduced false positives
Foundational layer: cyber model, workspaces, and integration backbone to DevOps toolchain
Out-of-the-box and customizable workflows for regulatory and security processes
Centralized compliance management with evidence generated from live data