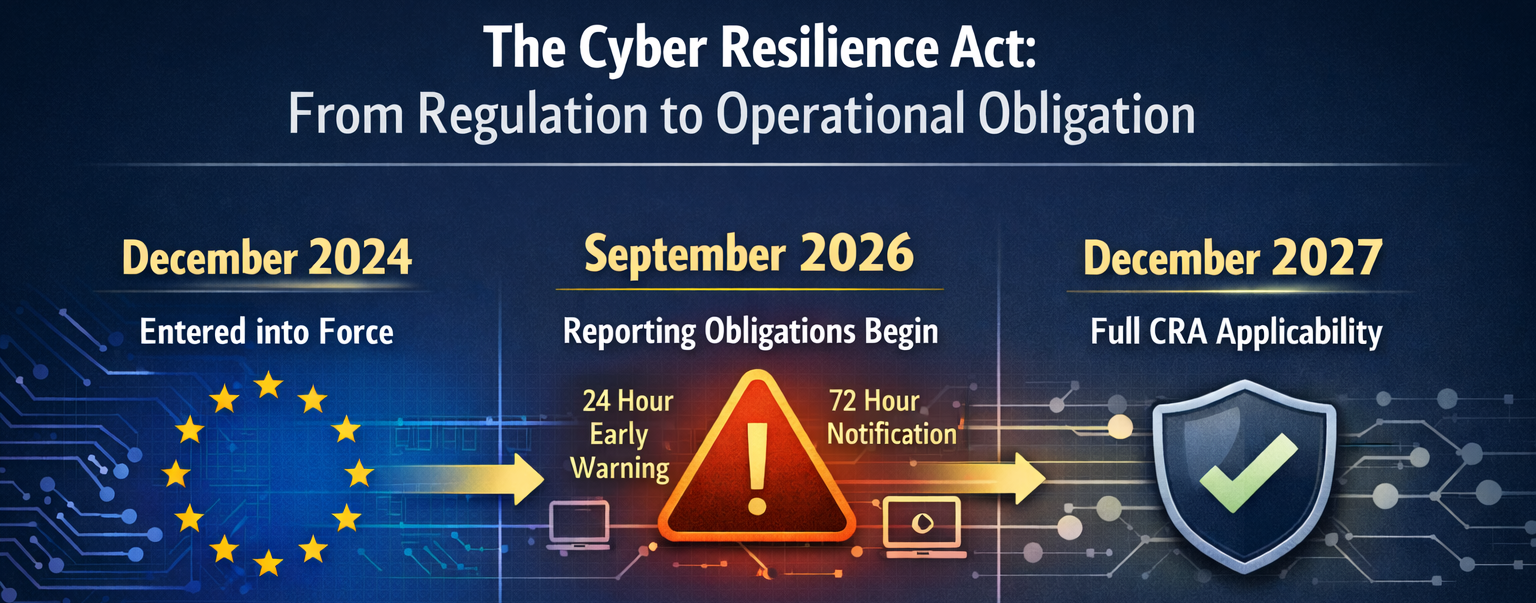
The CRA Clock Is Ticking: What Manufacturers Need to Do Now
The Cyber Resilience Act establishes cybersecurity requirements as a condition for placing products with digital elements on the European market, with phased obligations beginning in
" " indicates required fields

The Cyber Resilience Act establishes cybersecurity requirements as a condition for placing products with digital elements on the European market, with phased obligations beginning in
Why February 2, 2026 was not just another regulatory date February 2, 2026 marked a watershed moment for the medical device industry. On that date,
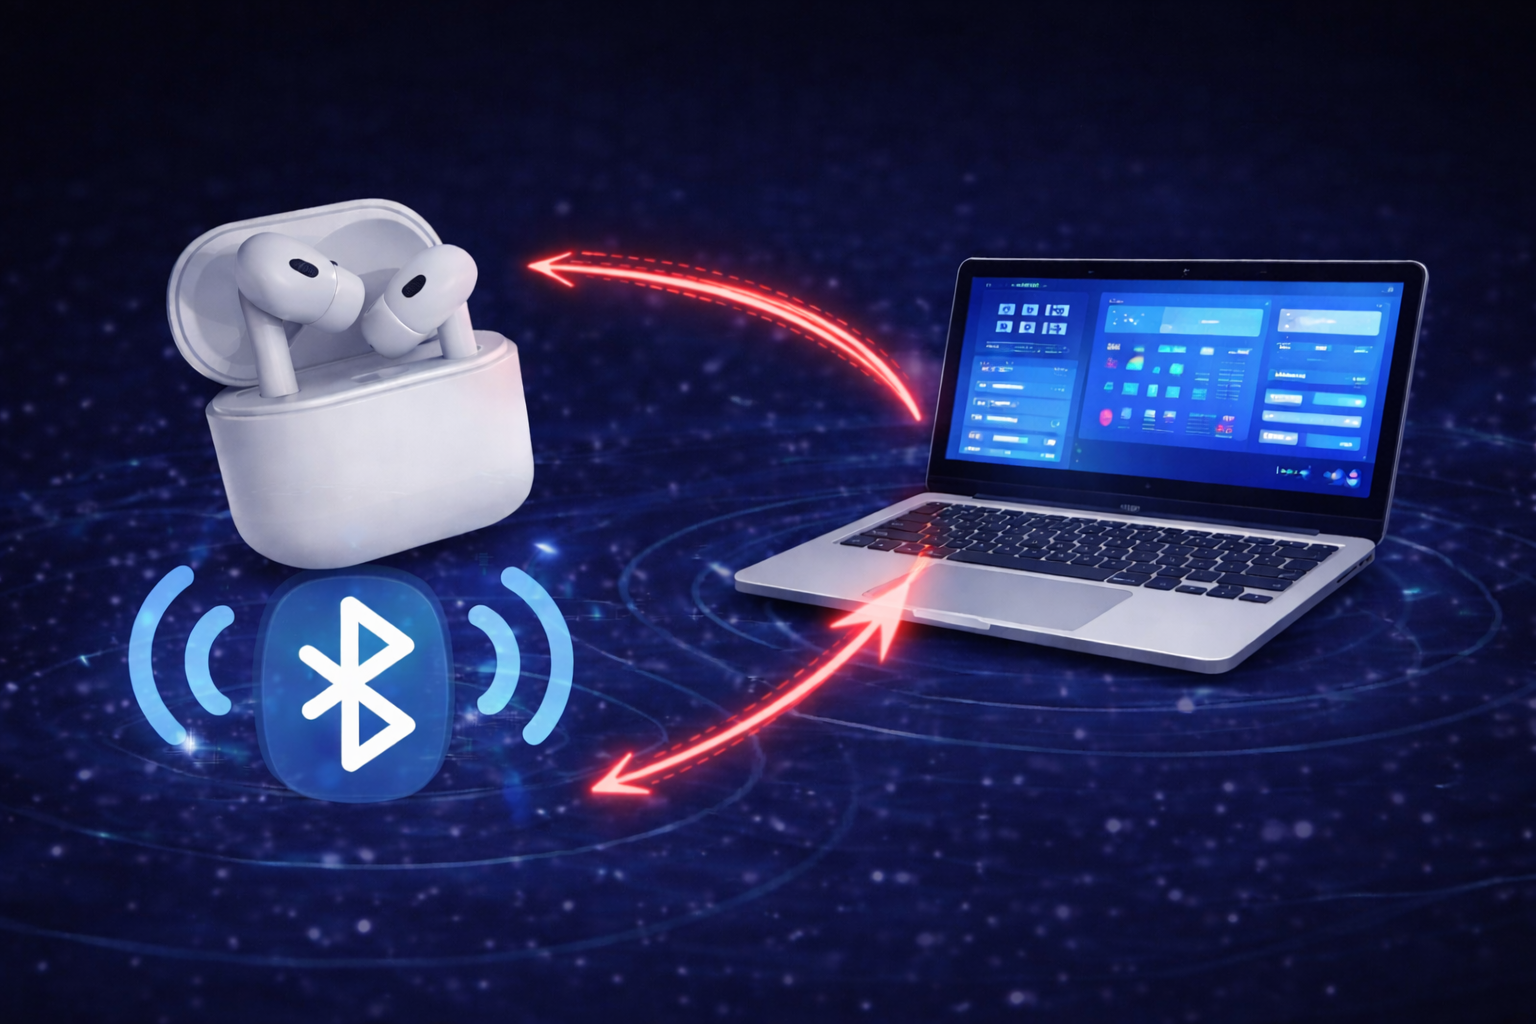
CVE-2025-36911, widely known as “WhisperPair,” recently exposed a critical class of vulnerabilities in Bluetooth audio accessories that rely on Google’s Fast Pair protocol. But here
The recent FDA Class I recall and safety alert involving Abiomed, Inc.’s Automated Impella Controller (AIC), due to cybersecurity vulnerabilities, is a powerful reminder that
The acquisition delivers faster compliance, stronger supply-chain security, and unparalleled MedTech expertise, while positioning C2A Security for accelerated global growth Featured Assets C2A Security Acquires
The partnership will leverage EVSec platform with HARMAN’s Automotive Engineering Services capabilities to automate compliance and regulatory monitoring with US DoC 791D Rule Jerusalem, Israel,
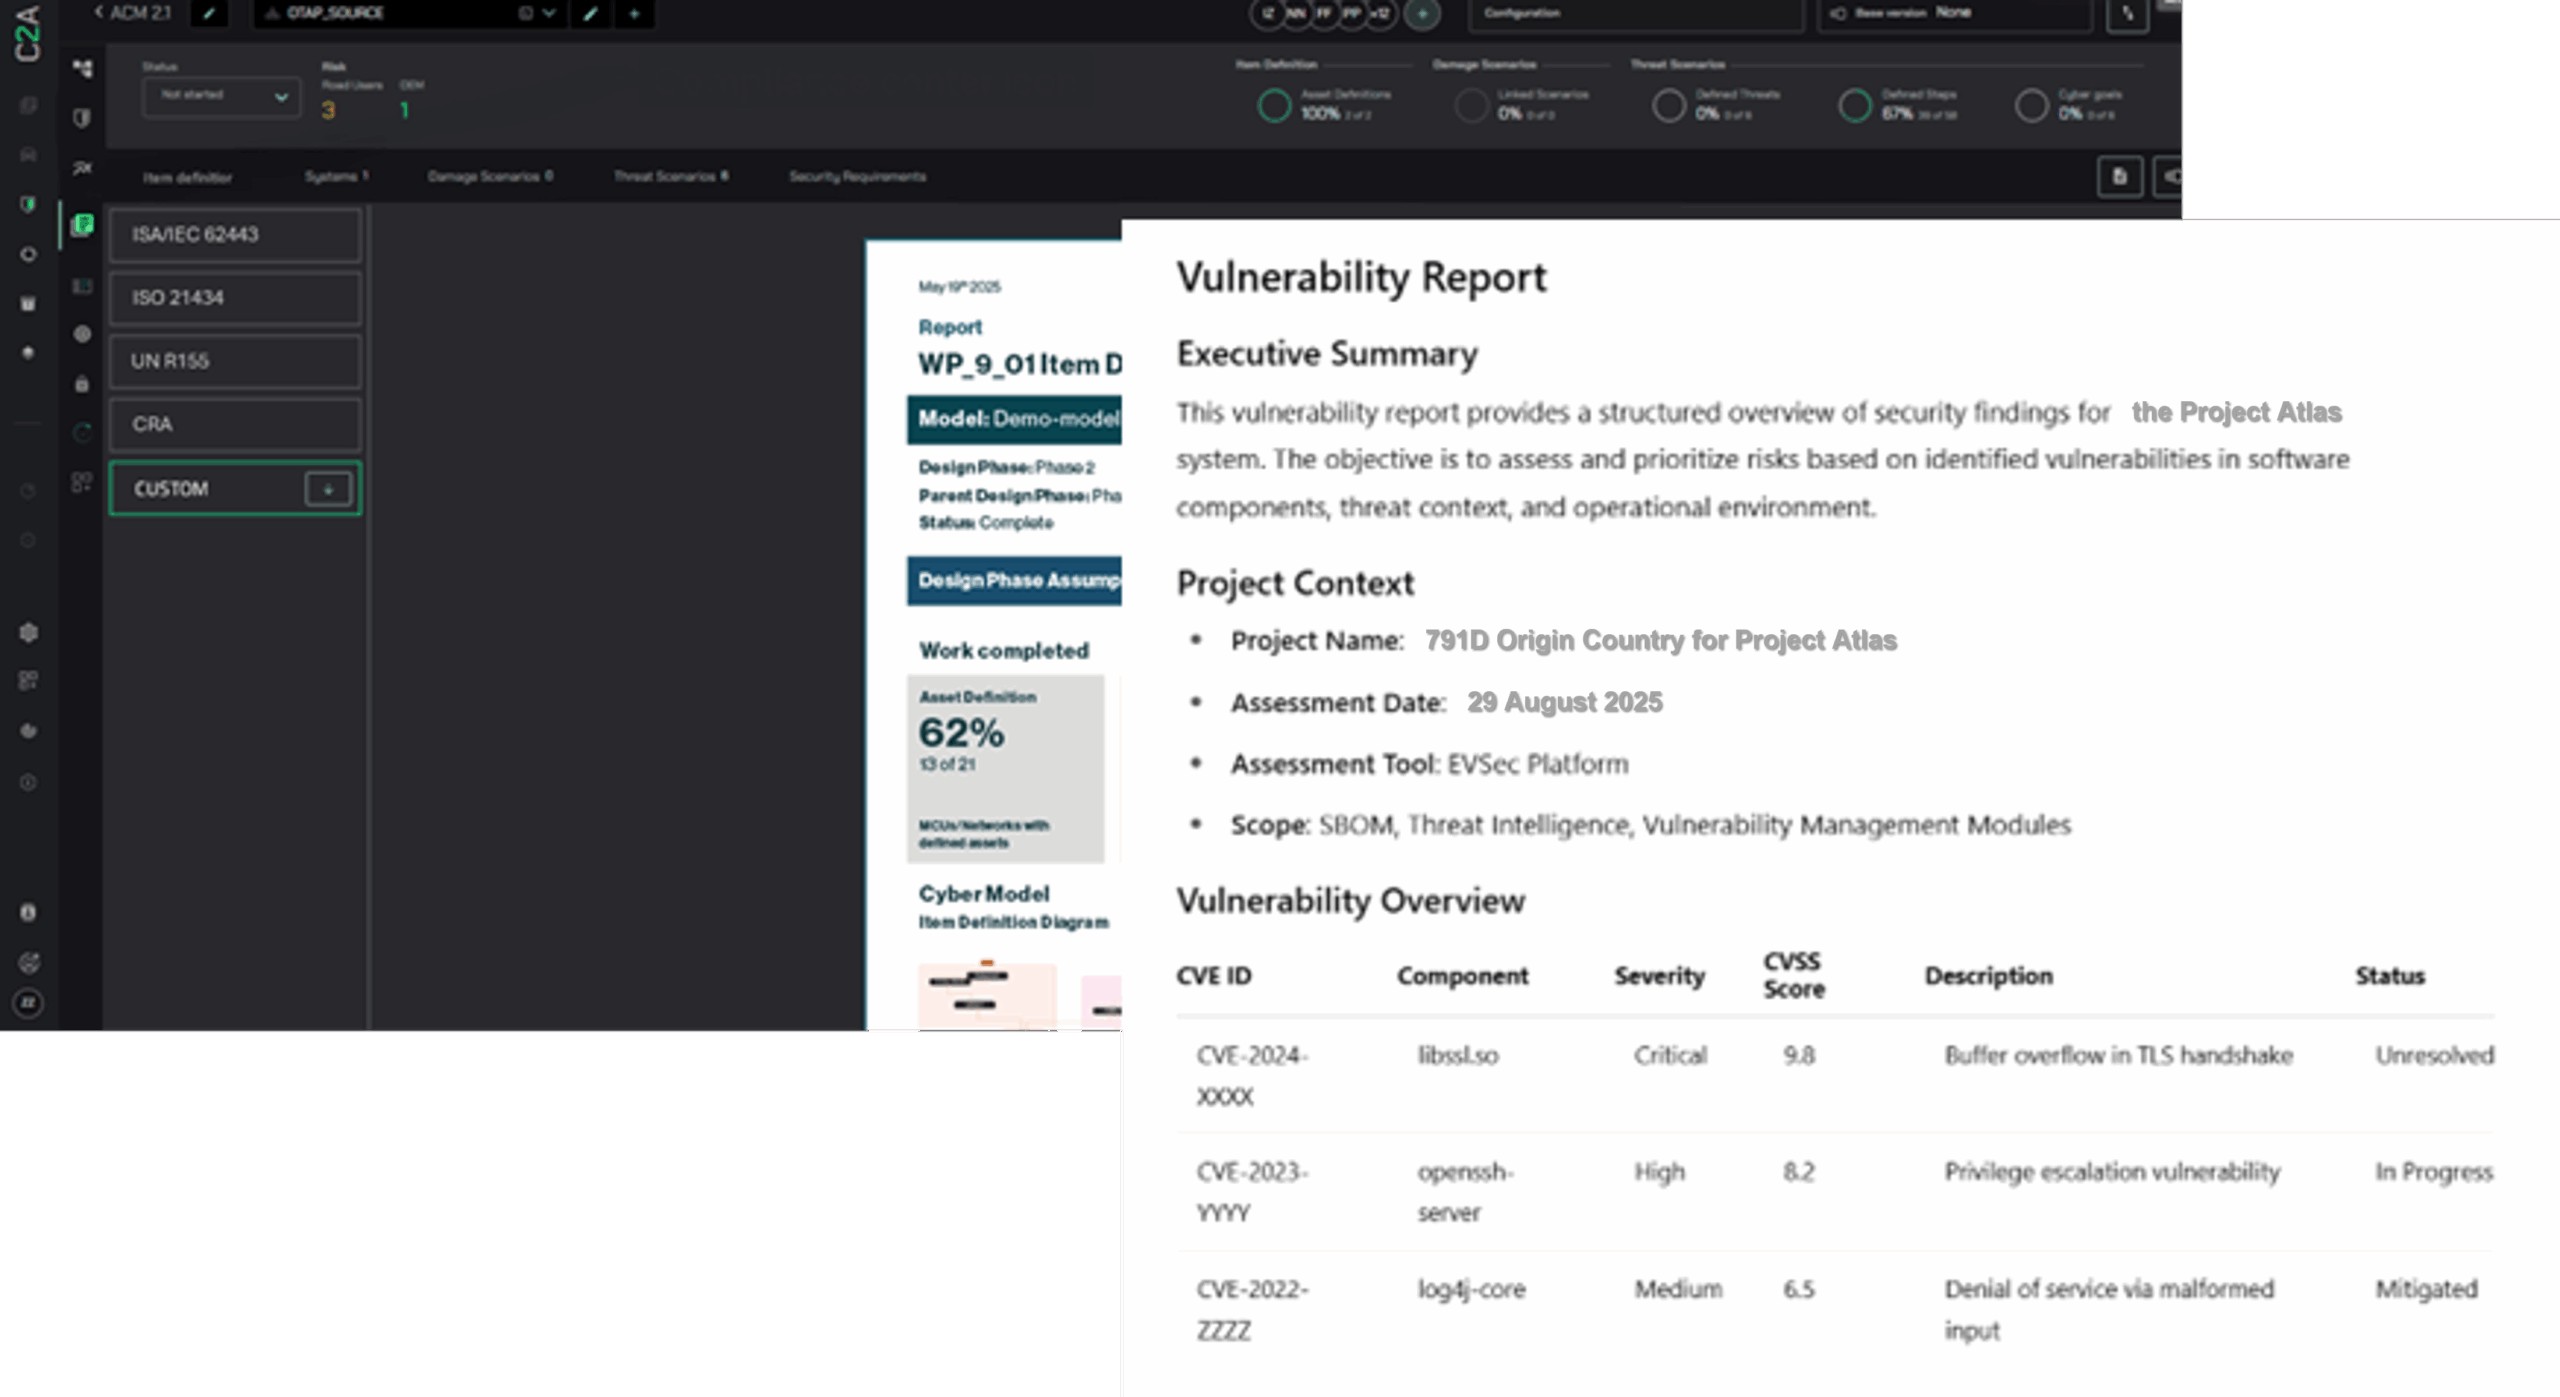
The new capability is designed to give organizations the tools and automation they need to meet regulatory requirements quickly, confidently, and without slowing innovation Jerusalem,
What is an SBOM and why is it Important? A Software Bill of Materials (SBOM) is a foundational cybersecurity and compliance artifact that provides a
Why The New FDA Update Matters Right Now for MDMs The FDA’s Final Cybersecurity Guidance of June 2025 introduces significant new requirements under the FD&C